Understand what applies to your organisation. Assess business and technology risks. Connect findings, controls, evidence and decisions across your enterprise.
Approved organisational facts, canonical Master Controls and evidence can be reused across relevant obligations and workflows, subject to semantic coverage and permission.
Each capability shows what it does, how AIRRP does it differently, why a customer would choose it, and an example from the product. All six work from the same governed enterprise information.
01
Compliance Management
What it does
Helps organisations identify relevant laws, regulations and frameworks, determine the requirements applicable to their context, and manage assessments against governed controls and evidence.
How it works differently
Reuses approved enterprise facts rather than starting from a generic questionnaire for every framework. Connects requirements to shared Master Controls, evidence expectations and explainable applicability decisions.
Why a customer would choose it
Less repeated interpretation and collection work; more consistent, traceable compliance assessments across programs.
Enterprise context
Applicable requirements
Governed controls and evidence
Assessment and decisions
Product proofProduct screen
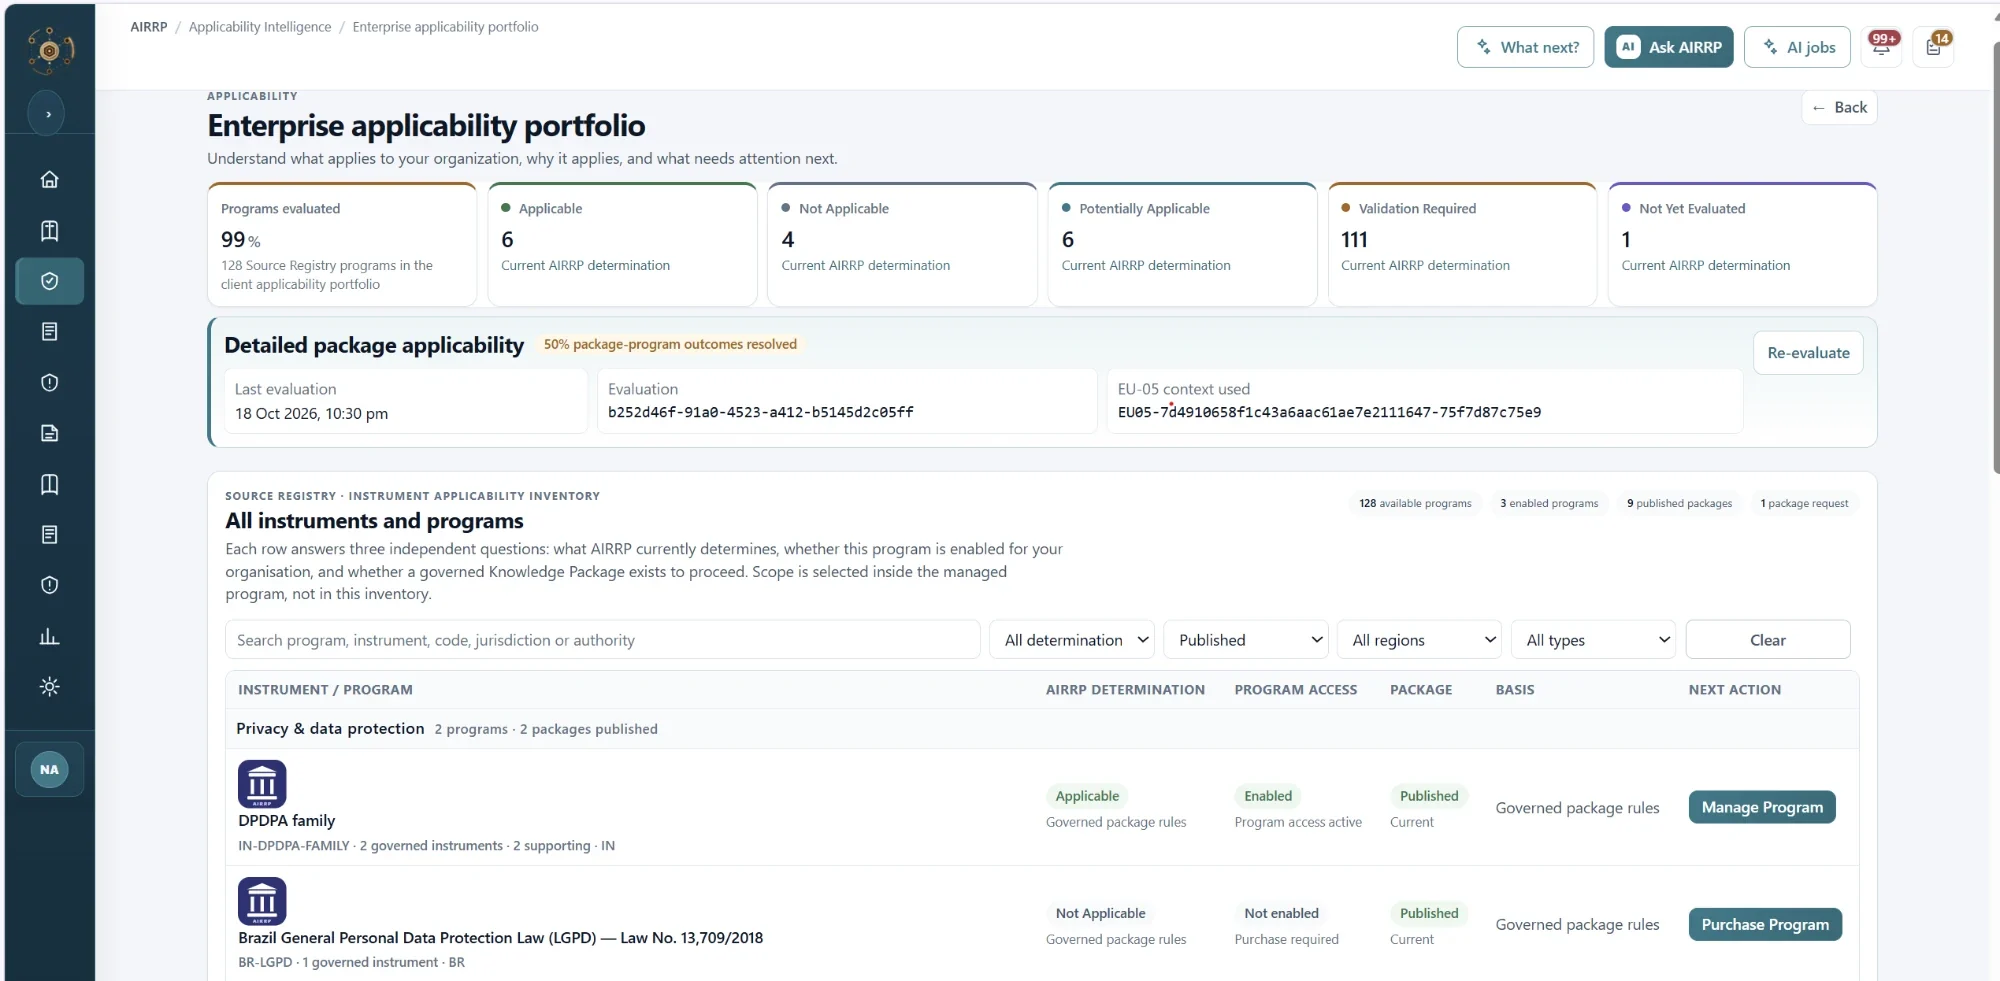
View full screenAIRRP shows what applies to the organisation and why: here, 6 programs applicable and 4 not applicable, each with its recorded basis.
02
Risk Assessments
What it does
Supports assessment of business processes, AI applications, networks, servers, cloud environments and other in-scope business or technology subjects.
How it works differently
Uses the actual assessment subject and available enterprise context to select relevant controls, evidence and questions; links assessment findings to risk decisions instead of leaving assessments as isolated checklists.
Why a customer would choose it
More relevant assessments, clearer gaps, and an actionable connection from findings to risk management.
Select subject
Understand scope and dependencies
Assess controls and evidence
Findings and risk decisions
Product proofCapture pending
Will show: a real assessment subject — such as a business process, AI application or server — its tailored scope and control checks, and an attributable finding.
03
Centralised Enterprise Risk Register
What it does
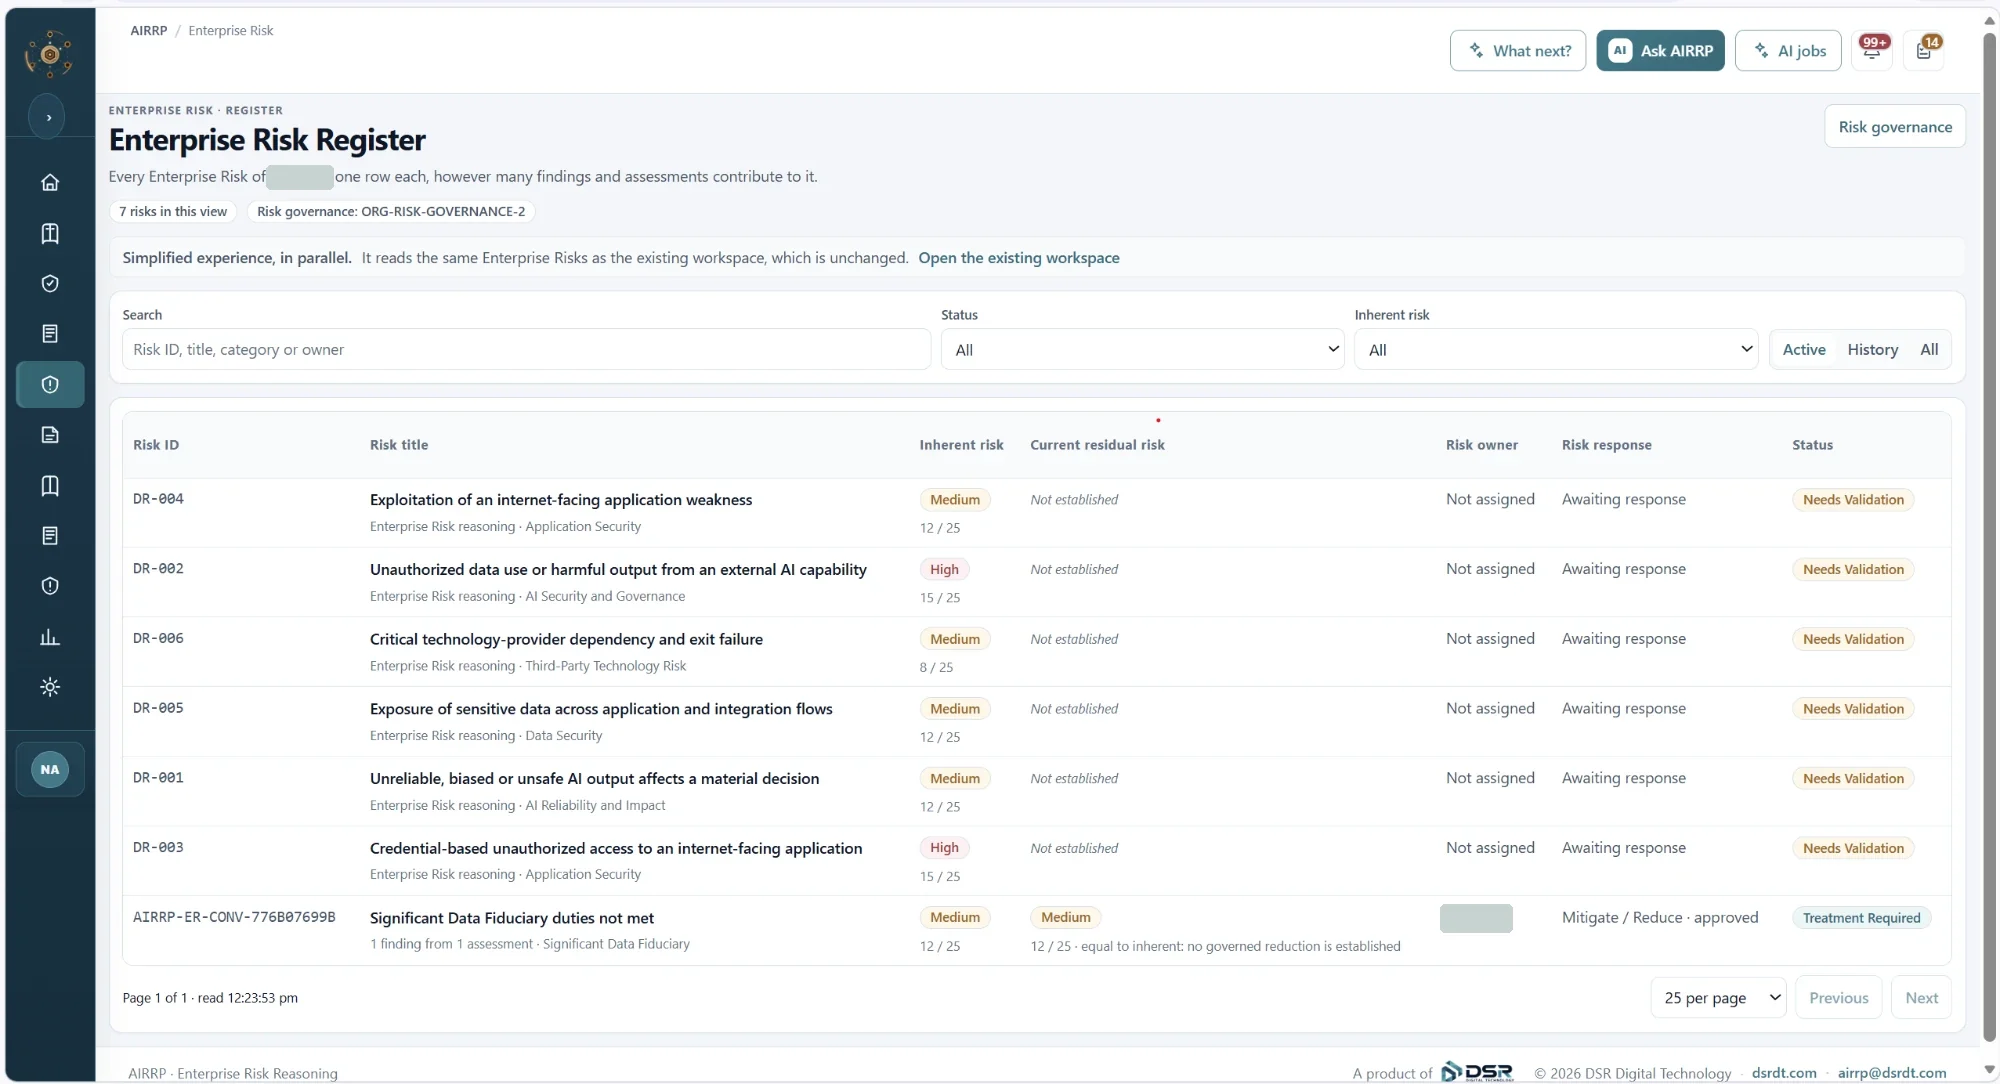
Brings risks identified through different assessments and business activities into one enterprise risk register, with ownership, evaluation, treatment and tracking.
How it works differently
Preserves the connection between source findings, affected subjects, risk reasoning, human decisions and treatments rather than maintaining detached risk entries.
Why a customer would choose it
Better enterprise-wide visibility, less duplicate reporting and clearer accountability for risk decisions.
Findings and risk inputs
Governed risk assessment
Owner/decision
Treatment and tracking
Product proofProduct screen
View full screenEach risk carries its source, owner, approved response and treatment status. Risks without an owner stay visibly “Needs Validation”.
Coming soon04
Third-Party Risk Management
You assess your third parties
What it does
Supports third-party relationship understanding, qualification, risk assessment, due diligence, evidence review and risk tracking across the relationship lifecycle.
How it works differently
Uses known business context and existing enterprise knowledge where available, reducing repeated requests for information and connecting third-party risks to the enterprise view.
Why a customer would choose it
More contextual vendor risk decisions and less fragmented third-party assurance work.
Identify governed third-party relationship
Establish business context
Assess and review
Track risk and follow-up
Product proofComing soon
Third-Party Risk Management is coming soon. Product screens will be added when it is released.
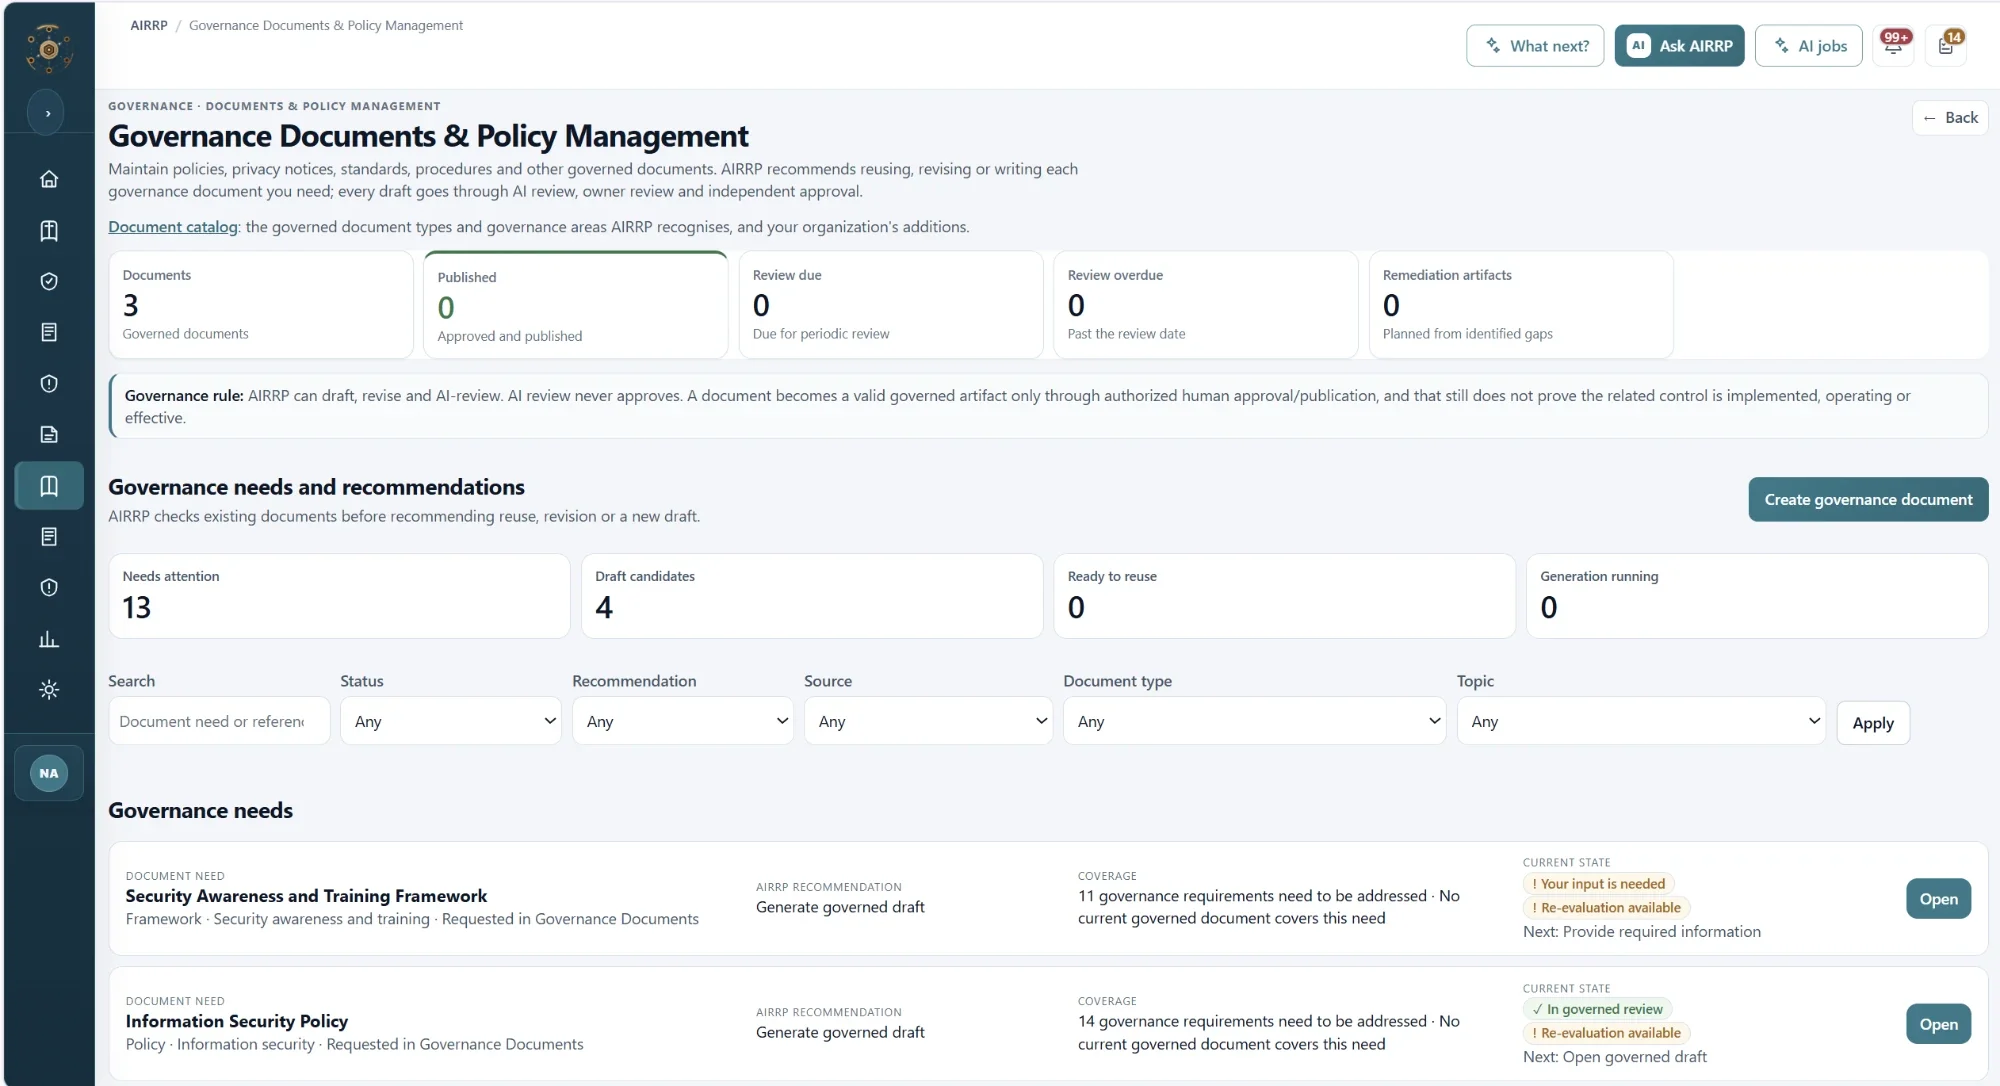
Builds drafts using governed organisational facts and available regulatory/control context, followed by review and approval instead of producing generic, context-free templates.
Why a customer would choose it
Documents can be more consistent with the organisation’s actual environment, reducing drafting effort and rework.
Select document
Use governed knowledge
Draft
Review and approve
Product proofProduct screen
View full screenAIRRP checks existing documents before recommending reuse, revision or a new draft. Every draft goes through owner review and independent approval.
06
Customer Security and Compliance Questionnaire Assistance
Your customers assess you
What it does
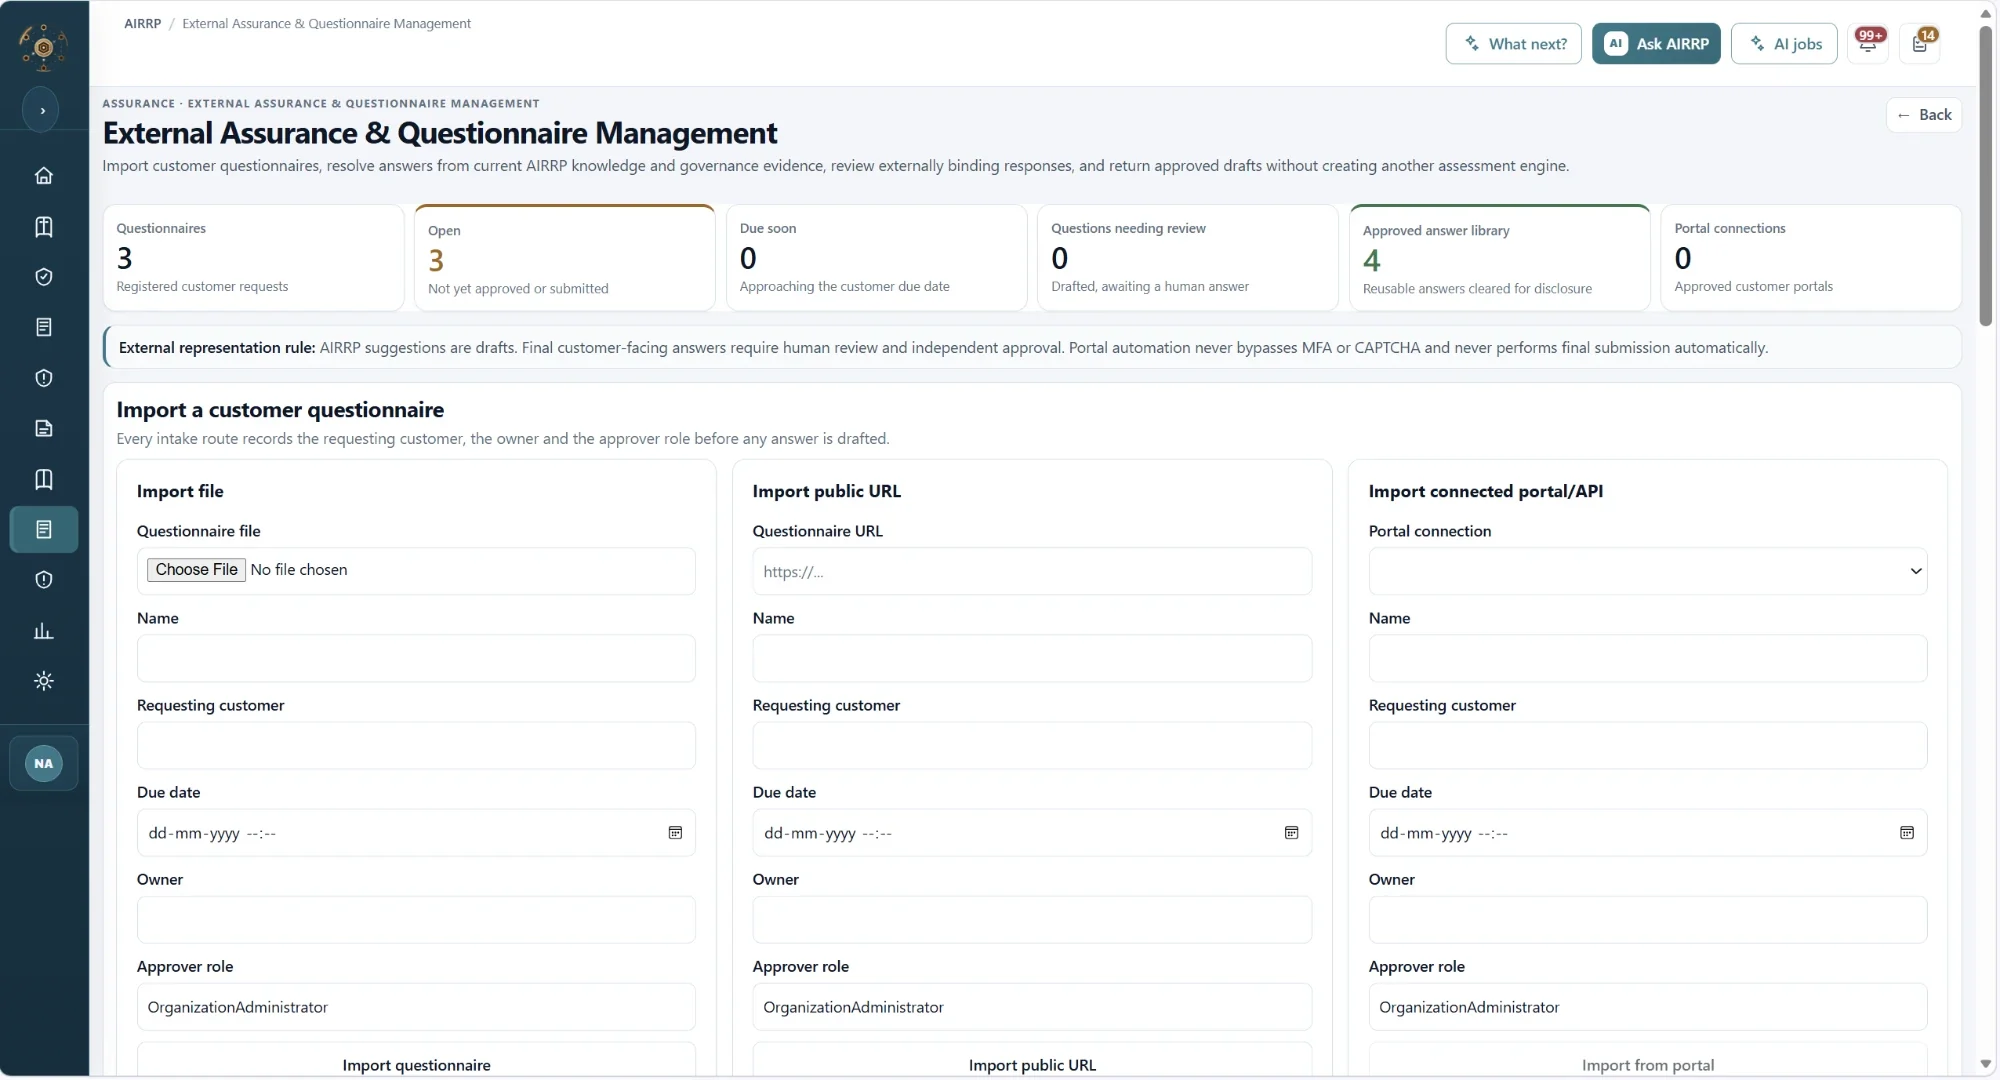
Helps organisations prepare responses to due-diligence, security, privacy and compliance questionnaires received from their own customers.
How it works differently
Draws on approved organisational facts, governance documents, controls and evidence already available in AIRRP, with human review of proposed responses.
Why a customer would choose it
Faster, more consistent customer assurance responses without repeatedly collecting the same information.
Receive questionnaire
Reuse approved information
Prepare responses
Review and finalise
Product proofProduct screen
View full screenAnswers are drafted from current AIRRP knowledge and evidence. Final customer-facing answers need human review and independent approval.
Product screens are from AIRRP, cropped for publication, with organisation and person names redacted. Select a screen to see it in full.
Two directions of assurance
Third-party risk and customer questionnaires are separate capabilities.
Third-Party Risk Management assesses your third parties. Questionnaire Assistance helps when your customers assess you. Each has its own workflow in AIRRP.
04 · Third-Party Risk Management · Coming soon
You assess your third parties
Your organisationThird party
Qualify, assess and track the risk of relationships you depend on.
06 · Questionnaire Assistance
Your customers assess you
Your customerYour organisation
Prepare reviewed responses to the questionnaires your customers send.
One connected example
One application, understood once, informing every connected decision.
How one business application moves through AIRRP, from understanding it once to reusing that knowledge.
Coming soon A worked example with product screens: an Employee HR Management System that handles workforce personal data.
1
Understand once
Record the application, business owner, processing context, connected systems and relevant third-party relationships.
Business owner
Processing context
Connected systems
2
Determine obligations
Use that context to identify applicable requirements and reuse the appropriate governed controls and evidence.
Applicable requirements
Reused Master Controls
Evidence expectations
3
Assess and decide
Evaluate control and evidence coverage for the application, and link material findings to the enterprise risk register and human decisions.
Coverage gaps
Risk register
Owner decision
4
Reuse governed knowledge
Relevant approved facts support governance documents and customer questionnaire responses, each with human review.
Privacy notice
Policies
Customer questionnaires
5
Third-party path
The external provider’s relationship is reviewed in Third-Party Risk Management and its risk joins the same enterprise view.
Third-party relationship
Risk review
The same governed enterprise information informs multiple connected decisions — less repeated entry and less disconnected work. People review and approve each material decision.
Why choose AIRRP
Why connected work matters
You are paying for connected decisions, governed reuse and traceability — not simply another six-module feature list.
Disconnected work compared with AIRRP’s governed, connected approach
When work is disconnected
AIRRP’s governed, connected approach
Practical buyer value
Enterprise facts collected again for each activity
Reuse approved enterprise context where relevant
Less repeat collection and inconsistent answers
Similar requirements assessed in separate silos
Reuse semantically sufficient canonical controls and evidence
More consistent coverage and a traceable assessment trail
Findings become detached spreadsheet entries
Link findings to enterprise risk ownership, decisions and treatment
Clearer accountability and follow-through
Documents and questionnaires start from scratch
Reuse relevant approved facts, documents and evidence with human review
Reduced rework and more consistent assurance responses
Required approvals and manual checks stay in place. Pricing follows below.
Pricing
What you pay for, and why.
AIRRP is priced per program, per governed application and per governed third party, charged annually and excluding GST. Users and reassessments are unlimited. The capabilities included are confirmed in your licence scope.
AIRRP annual pricing by charging unit
Charging unit
Price
Charged per
Term
Common compliance programse.g. ISO/IEC 27001, NIST CSF, CIS Controls
₹8,00,000
Program
Annually
Privacy, regulatory and specialised programse.g. DPDPA, EU GDPR, UK GDPR, RBI and SEBI cybersecurity requirements
₹10,00,000
Program
Annually
NIST SP 800-53
₹25,00,000
Program
Annually
Governed applications
₹10,000
Application
Annually
Governed third parties
₹20,000
Vendor
Annually
Professional services
Quoted separately
All prices exclude GST. Framework examples are illustrative; the programs available to you are confirmed in your licence scope.
Included
Unlimited users and reassessments.
No separate legal-entity fee, hidden platform fee or per-control, evidence, finding, risk or document charge.
20%
Founding-customer discount
20% on eligible compliance programs only.
Need a quote for your scope?
Tell us how many programs, applications and third parties you plan to govern, and we’ll prepare your quote.
 View full screen